Product engineering · 7 Oct 2026 · 5 min read
Privacy-first architecture for consumer apps, in plain language
If the data never leaves the device, you do not need to ask people to trust you with it. A short guide to the choices that make a consumer app private by design.
Privacy is often handled as a page of text. The app collects what it wants, and the policy explains why. Users do not read it, and they do not trust it.
A better approach is to make privacy an architecture decision. The app is private because of how it is built, not because of what it promises.
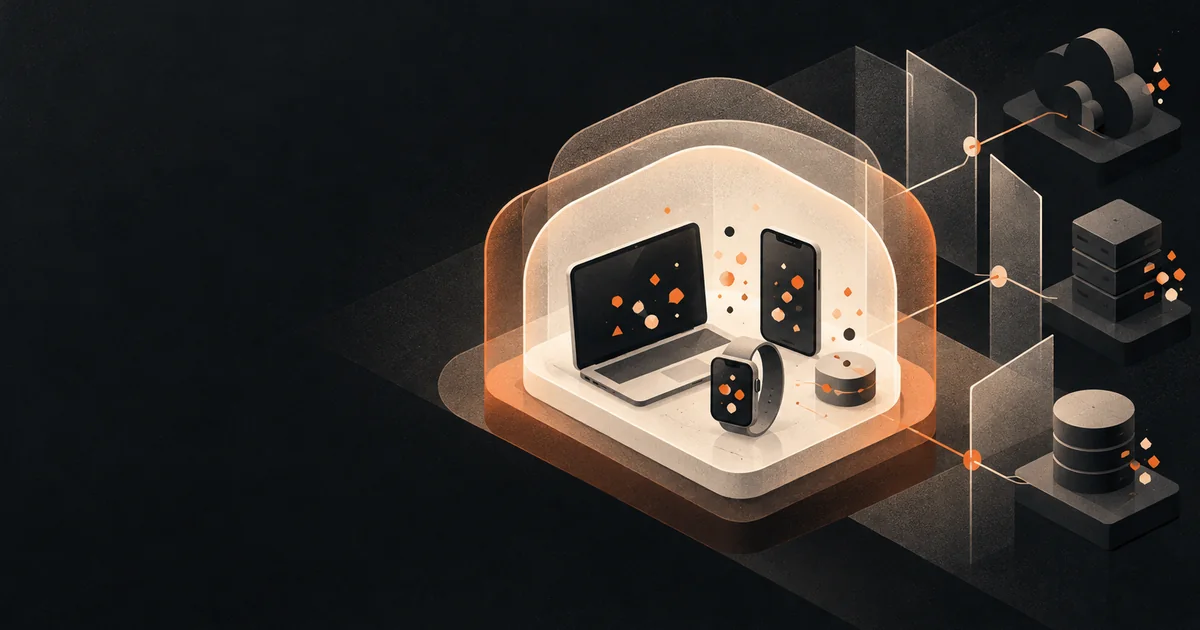
Process on the device when you can
Photos, voice, documents and location are the data people care about most. Modern browsers and phones can process all of them locally.
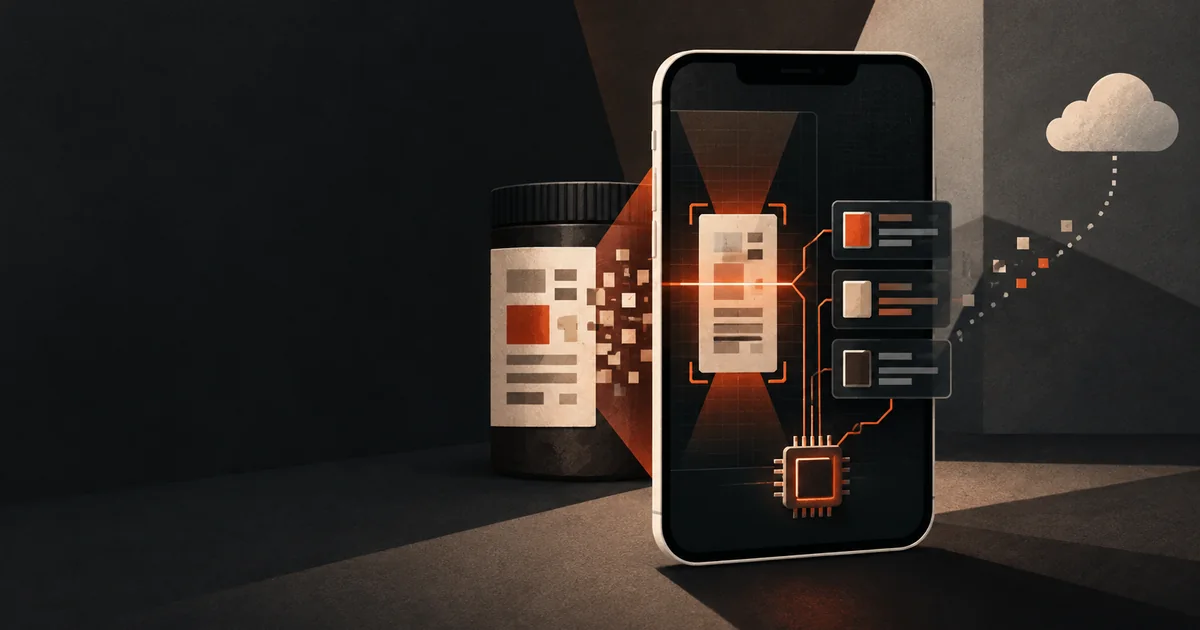
A label-reading tool can run OCR in the browser while voice input uses the device’s own speech capability. The photo and recognised text never need to leave the phone. There is no image server to secure, no upload to explain and no processing cost for each scan.
The trade-off is speed and engineering effort. Local processing is slower at first, and the team has to make it fast. That work is worth it. It removes the trust question entirely.
Do not require an account
An account is a database of personal data that you now have to protect. Ask whether the product needs one. A planning tool can save a plan to the device, or export it as a file, without ever knowing who the user is.
A family planning a complex trip can complete a questionnaire, download the plan and take it to an adviser without creating an account. The site does not need to know who they are.
Accounts should be justified by a user benefit, not by a desire to collect leads. Synchronisation across devices, paid access or collaboration may require identity. Saving one plan on one device often does not. Start with the task and add identity only when the task cannot work without it.
Collect the minimum, and say so
When the product does need data, collect the least that works, and explain in plain words what happens to it. A consent banner that says “no ads, no profiling, nothing sold” is short because the architecture made it short.
Data minimisation applies to fields as well as events. Do not ask for a full name when an email address is enough. Do not request a date of birth when an age range answers the product question. Do not keep an uploaded file after extracting the small piece of information the feature needs.
Retention is part of collection. A database that keeps everything forever is collecting more than the product needs, even if each individual field looked reasonable. Set deletion periods, document them and make sure backups follow the same policy.
Separate what you store from who sent it
Feedback, ratings and analytics are useful. They do not need to be tied to a person. Store the event and the page. Do not store the identity unless the feature cannot work without it.
Use aggregate questions whenever possible. The team may need to know which step fails most often, not which named person failed there. A random session identifier can connect a short sequence of events without becoming a permanent profile. Avoid device fingerprinting and cross-site tracking; neither is necessary to improve a focused product.
Keep sensitive systems separate
When personal information is unavoidable, isolate it. Contact details should not live in the same table as behavioural analytics merely because joining them is convenient. Use separate stores, narrow access and explicit service boundaries. A breach of one system should not reveal the entire picture of a person.
Logs deserve the same scrutiny as databases. Error reports can accidentally capture form values, URLs, recognised text or access tokens. Review logging defaults, redact sensitive fields and keep production logs for a defined period. “We did not save it” is not true if it remains in monitoring data for a year.
Design for failure cases
Privacy-first apps run into permission prompts: the camera is denied, the microphone is blocked, the device is offline. Each case needs a clear path. Offer manual input, explain why the permission was asked, and never block the core task.
Ask for permission at the moment it becomes useful. A camera prompt on page load feels invasive because the person has not chosen to scan anything. A prompt immediately after pressing “Scan a label” has context. Explain the benefit before the browser dialog appears, because the browser cannot explain the product’s intention for you.
Revoking permission should not break navigation or strand saved work. Provide instructions for changing the setting, but keep the manual route visible. Test these states deliberately; permission failures are normal product states, not rare technical exceptions.
Make deletion understandable
People should know what can be removed and how. If information stays only in the browser, say that clearing site data removes it. If the server stores an account, provide deletion inside the account rather than requiring an email. If legal or operational requirements prevent immediate deletion, explain the delay precisely.
Privacy controls work best near the feature they affect. A global policy remains necessary, but it should not be the only place where behaviour is explained. A one-sentence note beside an upload field can prevent more uncertainty than another page of legal language.
Why it pays
Products built this way are cheaper to run, simpler to secure and easier to explain. Users notice when an app does not ask for more than it needs. That is a feature, and it is one most competitors cannot copy quickly.
Privacy-first architecture also limits future temptation. A team cannot quietly repurpose information it never collected. That constraint keeps the product aligned when priorities, ownership or business models change.
Keep reading